 AML Global
 Luxembourg
 Belgium
 Ireland
 Malta
 Cayman Islands
 EU Regulations
 Cyber Security
 AML Courses
 Member Organisation 1
 Member Organisation 2
 Non-Profit Organisation
elearning Course: Cyber Security Awareness for Financial Services – Cayman Islands
€75.00 + Applicable VAT
A comprehensive course providing detailed insights, realistic scenarios, and practical tools to enhance cyber security awareness in financial services. Suitable for financial services professionals at all levels, from entry-level employees to senior executives; staff in banking, insurance, investment, and payments who handle sensitive client information or have access to internal systems.
This course is now available with instant access.
.
A comprehensive course providing detailed insights, realistic scenarios, and practical tools to enhance cyber security awareness in financial services. Covers the threat landscape, hacker tactics, data protection, authentication and password management, practical workplace scenarios, incident reporting responsibilities, and the Cayman Islands CIMA regulatory framework.
Suitable for all staff of CIMA-regulated entities, including banks and trust companies, securities investment businesses, money services businesses, insurers, building societies, fund administrators and virtual asset service providers, who handle client information or have access to firm systems
Learning Objectives:
By the end of this course, the learner will be able to:
- Understand why financial services is such an attractive target, and the CIMA and data protection rules that frame everything you do.
- Recognise the most common attacks and the red flags that give them away.
- Understand how attackers manipulate people, how to protect data and accounts, and how to respond when something goes wrong.
- For the Cayman Islands, know the role of CIMA and the other authorities you may need to involve.
Sections & Modules:
Module A — Recognising Cyber Threats and Hacker Tactics
Module 1: Introduction
1. Course Objectives
2. Why Cyber Security Matters in Financial Services
3. Types of Data Targeted by Cyber Criminals
4. High-Profile Cyber Incidents in Finance
5. Cyber Breach Impact
Module 2: Recognising Cyber Threats
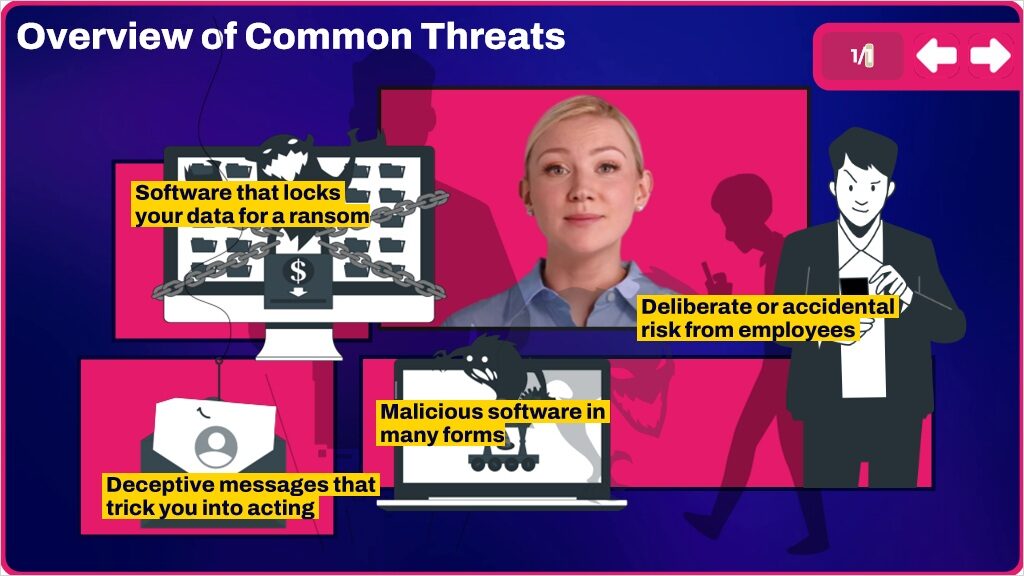
1. Overview of Common Threats
2. Deep Dive into Phishing Attacks
3. Bank Phishing Incident
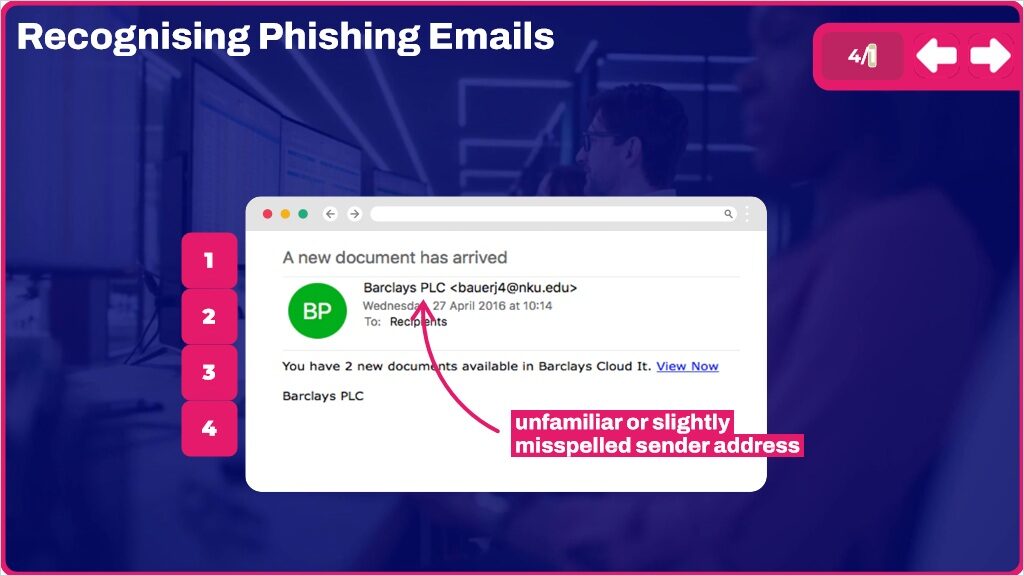
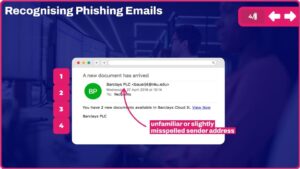
4. Recognising Phishing Emails
5. Indicators of Compromise
6. Insider Threats
7. Ransomware
8. Malware Threats
9. Best Practices for Identifying Threats
10. Reporting Cyber Threats
Module 3: Understanding Hacker Tactics
1. Psychology and Motivations of Hackers
2. Common Attack Vectors
3. Hacking Methods
4. How Criminals Monetise Stolen Data
5. Bank Malware Incident
6. Social Engineering Explained
7. Real-World Social Engineering
8. Prevention Through Awareness
9. The Importance of Regular Software Updates
10. Practical Advice
Module B — Protection, Authentication & Your Responsibilities
Module 4: Protecting Personal & Private Information
1. Principles of Data Protection and Privacy
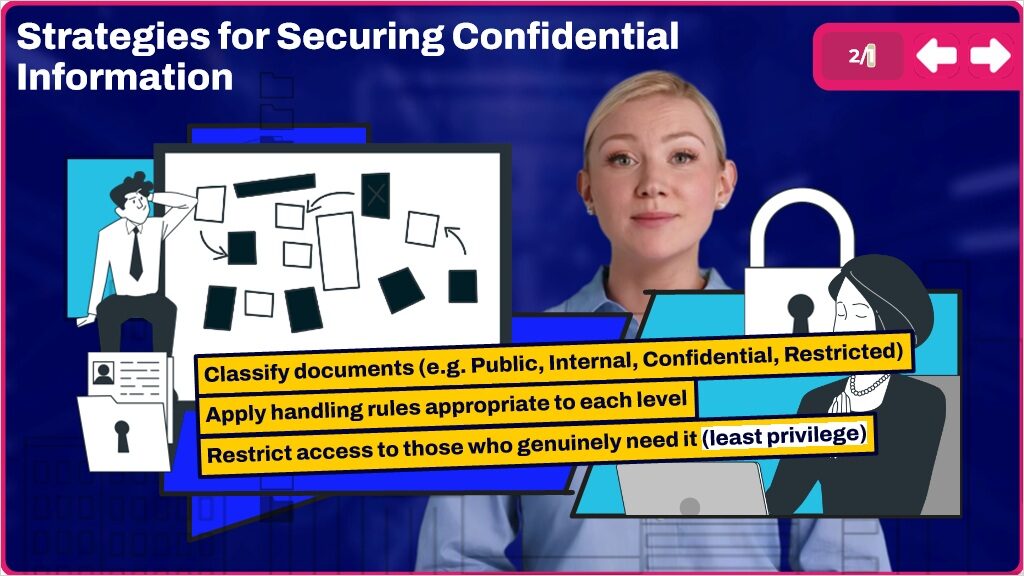
2. Strategies for Securing Confidential Information
3. Secure Data Handling Protocols
4. Encryption and Secure Communication
5. Common Data Protection Mistakes to Avoid
6. Data Leak Incident
7. Employee Responsibilities in Data Protection
8. How to Respond to Data Breaches
9. Practical Tips for Everyday Security
10. Data Protection Decisions
Module 5: Creating Strong Passwords & Authentication
1. The Critical Role of Strong Authentication
2. Anatomy of a Strong Password
3. Password Manager Tools and Best Practices
4. Multi-Factor Authentication (MFA)
5. Avoiding Authentication Pitfalls
6. Identify the Weak Passwords
Module 6: Best Practices
1. Step-by-Step Response Plans
2. Preventative Strategies
3. Contingency Planning
4. Regular Security Audits and Assessments
5. Employee Roles in Cyber Security
Module C — CIMA-Specific Requirements for Cayman Islands Financial Entities
Module 7: Cayman Islands Regulatory Landscape
1. Why Cayman-Specific Cyber Rules Matter
2. The Cayman Islands Monetary Authority
3. Where the Authority Comes From
4. The Rule and the Statement of Guidance
5. The Other Authorities You Need to Know
6. How Cayman Compares
Module 8: CIMA Cyber-Security Rule
1. The Five Functions the Rule Adopts
2. Identify
3. Protect
4. Detect
5. Respond
6. Recover
7. Who Owns It
Module 9: Incident Reporting in the Cayman Islands
1. Notifying CIMA
2. What Counts as “Material”
3. Notifying the Ombudsman
4. Two Clocks, Two Triggers
5. The Calls That Are Not to a Regulator
6. A Friday Afternoon in George Town
Knowledge Check:
There is a 10 question knowledge check at the end of the course with a standard pass mark of 80% and unlimited attempts. The 10 questions are drawn randomly from a larger bank of questions. Each attempt will draw a different mix of questions.
Course Length:
90 minutes + 10 minutes of questions.
Certificate:
The user will receive a certificate in pdf format upon successful completion of the course and knowledge check.
Licence Information:
Each purchase is for a licence for a single user. The user has access to all the course material for 6 (six) months via our web based elearning platform.
Reporting:
For volume purchasers (offline only), your nominated administrator will be able to download:
- A set of detailed reports in Excel format showing course completion data for all of your users; and
- Copies of all certificates.
Compliance Officer Reviews:
Our courses have been reviewed and approved by over 100 Compliance Officers and deemed appropriate for use by all of their employees. We regularly update the course material as regulations evolve.
Our Feedback (from our range of courses):
“It was a great experience to participate in a professional e-learning course.”
“Good presentation, interactive implementation makes education process more interesting.”
“Very clear and well structured. The examples are excellent!”
Course Customisation (optional):
We can customise this course for your organisation. Customisation can include:
- Branded website and course
- Branded certificates
- Additional material covering your organisation and its AML policy and procedures
| License | Single User (Instant Access), Multi-User (Offline Processing) |
|---|
How to Order
Ordering from our site is very easy !
Online Orders:
Simply add the required courses into your shopping cart and then proceed to the checkout. You can pay by bank transfer or by credit/debit card.
If you pay by bank transfer, we will send your course login instructions once we have received the funds on our account.
If you pay by credit/debit card, we will send your login details as soon as we have setup your account (during normal working hours Monday to Friday). Orders received on weekends and bank holidays will be processed on the next working day.
Offline Orders:
If you prefer to order offline, you can do so as follows:
Send us an email to orders@governancepeople.com and include the following data:
- The name(s) of the course(s) that you wish to order.
- The First Name, Family Name and Email Address of the user(s) for each course.
We will then send you an invoice by email that will allow you to pay for your course by bank transfer or credit / debit card.
Volume Orders
For each course user we need the following information:
- First Name
- Family Name
- Email Address
You can add this information to the order at the checkout or send us a spreadsheet after you have completed your order. The email address to send the file is:
orders@governancepeople.com
Related products